February 27, 2025
Introduction
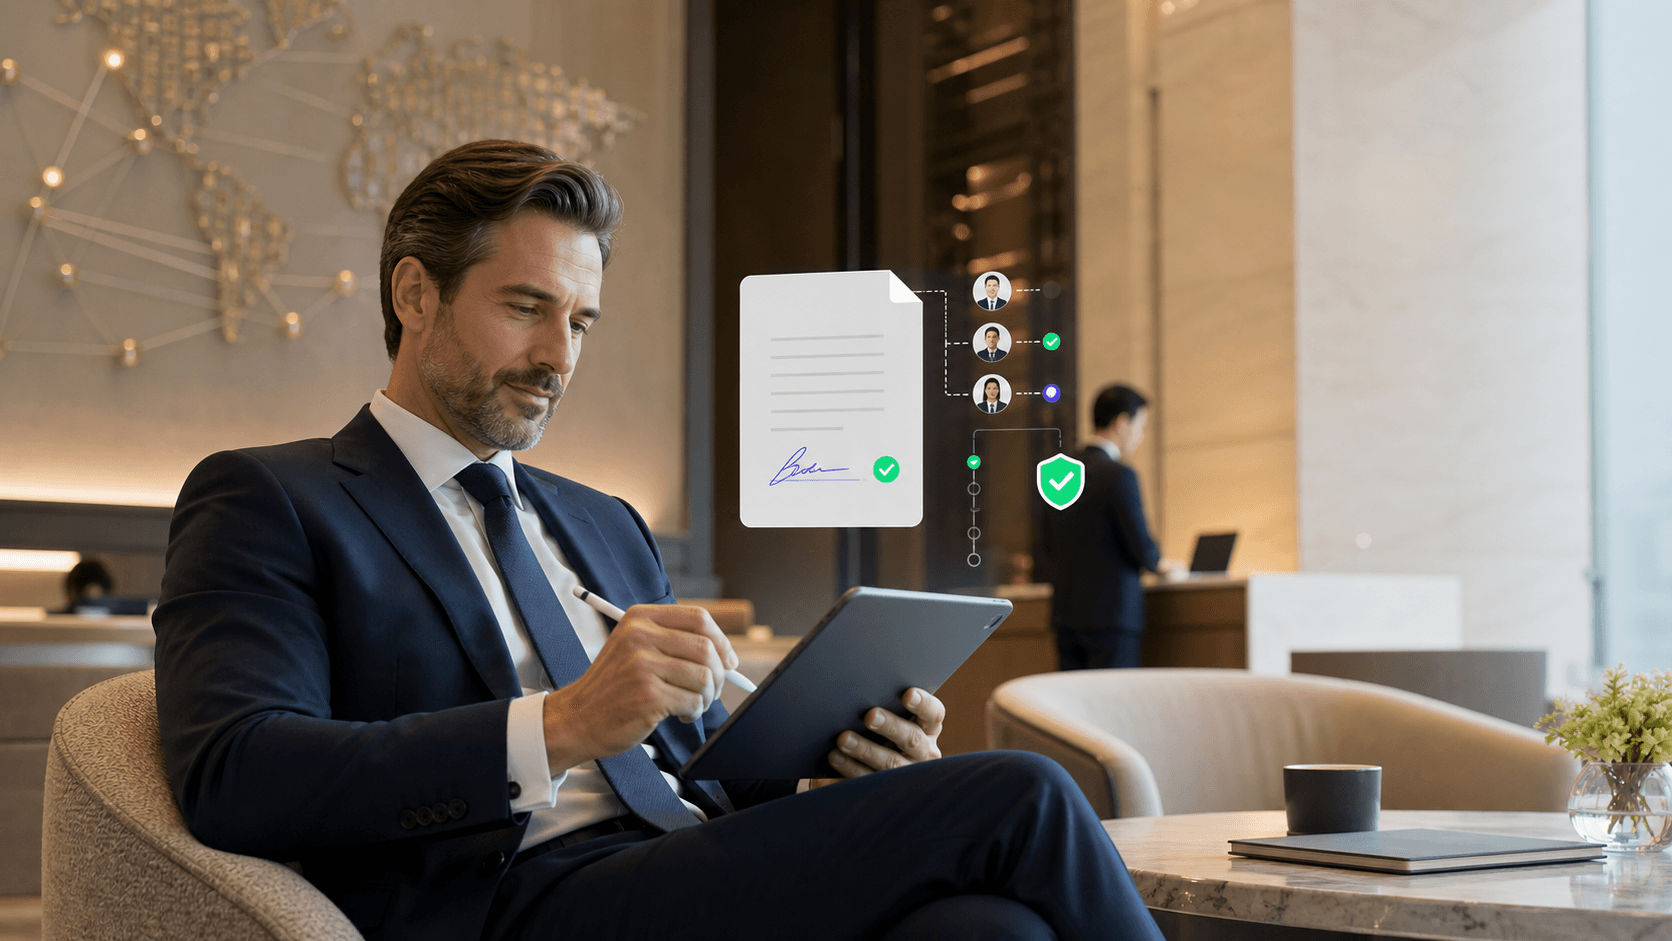
Digital signature verification means checking whether the signer certificate is trusted, whether the document changed after signing, whether revocation and timestamp evidence can be validated, and whether the signing record supports the business decision. A green check in a PDF viewer is useful, but it is not the whole review. Teams also need audit trails, signer identity evidence, record retention, and regional compliance checks before relying on a signed agreement.
This guide explains how to verify a digital signature in a practical business workflow, what each verification signal proves, where manual checks fall short, and when a platform such as Nota Sign is a better fit for repeatable cross-border signing.
Understanding Digital Signatures in Business
A digital signature is a cryptographic method for protecting authenticity and integrity. It is different from a drawn signature image or a simple click-to-sign action because it can connect the signed content to a certificate, a key pair, and a validation result. NIST explains in FIPS 186-5 that digital signatures are used to detect unauthorized data modification, authenticate the signatory, and provide evidence that the claimed signer generated the signature.
For a business document, verification usually needs to answer five questions:
- Who signed? The certificate and identity evidence should connect the signature to a signer or organization.
- Was the document changed? The signature validation result should show whether the file was modified after signing.
- Was the certificate trusted at signing time? The certificate chain, issuer, validity period, and revocation status matter.
- When was it signed? A trusted timestamp or reliable signing-time evidence helps support later review.
- Can the workflow be defended later? Audit trails, authentication records, signed-document retention, and exportable evidence decide whether the signature can be reviewed by legal, compliance, or a counterparty.
This is why digital signature verification is broader than opening a file and looking for a visible signature. If you are still separating concepts, Nota Sign's digital signature vs. electronic signature guide explains the difference between intent-based e-signing and certificate-backed digital signing.
How to Verify if a Digital Signature Is Authentic
Use the steps below for signed PDFs, high-value contracts, cross-border agreements, finance approvals, HR records, procurement documents, and other audit-sensitive files.
- Examine the signature certificate and format. Check whether the file contains a real digital signature field or only a visual signature image. Then inspect the signer certificate, issuer, validity period, trust path, and signing format.
- Use built-in or native verification tools. Open the file in a signature-aware PDF viewer or document system that can read certificate status, document-change history, validation details, and signature coverage. The tool should show whether the signature is valid, invalid, unknown, or only partially valid.
- Validate trust, revocation, and timestamp evidence. Review whether the certificate chains to a trusted authority, whether OCSP or CRL data is available, and whether the signature includes reliable timestamp evidence. A certificate may expire or be revoked after signing, so signing-time evidence matters.
- Assess legal and regulatory fit. Compare the technical result with the document type, jurisdiction, signer identity requirements, and retention rules. Technical validation does not replace legal review for regulated, cross-border, or high-value documents.
- Review the audit trail and signing record. For platform-generated agreements, review the sender, signer, email or phone verification, IP address, timestamps, consent events, completion status, and downloaded certificate of completion.
- Escalate high-risk documents. If the document involves regulated transactions, government filings, cross-border counterparties, corporate authority, high-value payment terms, or future litigation risk, route it to legal or compliance review.
Verification Checklist and Common Pitfalls
| Checkpoint | What to review | Why it matters | Risk if missing |
|---|---|---|---|
| Signature status | Valid, invalid, unknown, or partially valid result | Gives the first technical signal | A visual signature may be mistaken for a verified signature |
| Certificate issuer | CA or trust service provider | Helps connect the signer to a trust chain | Unknown issuer weakens reliance |
| Certificate validity | Start date, expiry date, and signing time | Confirms whether the certificate was valid when used | Expired or mistimed evidence can create disputes |
| Revocation data | OCSP or CRL response | Shows whether the certificate had been revoked | Missing revocation data leaves a trust gap |
| Document integrity | Whether content changed after signing | Confirms tamper evidence | Modified documents may lose evidentiary value |
| Timestamp | Trusted timestamp or reliable signing-time evidence | Supports later validation | Device-only time can be easier to challenge |
| Audit trail | Sender, signer, authentication, IP, event history | Connects the cryptographic result to the workflow | Technical signature may lack business context |
| Record retention | Final signed copy and exportable evidence | Supports legal, compliance, and counterparty review | Evidence may be unavailable when needed |
The most common verification mistake is treating a visible signature as proof. A name, stamp, or drawn signature on the page may show intent, but it does not prove certificate trust, tamper evidence, revocation status, or signer authentication.
| Pitfall | Why it matters | Better practice |
|---|---|---|
| Only checking the visual signature | A signature image can be copied or inserted without certificate evidence | Inspect the certificate, signature status, and document-change history |
| Ignoring certificate trust | Unknown or self-signed certificates may not support business reliance | Confirm issuer, trust path, validity period, and trust-service context |
| Skipping revocation status | A certificate can be revoked before expiry | Look for OCSP or CRL evidence and treat missing data as incomplete |
| Relying only on device time | Local device time can be weak evidence | Prefer trusted timestamp evidence where available |
| Losing the audit trail | Technical validation may not show who authenticated or approved | Preserve the platform audit trail and completion certificate |
| Treating technical validity as legal certainty | A valid signature can still fail a document-type or jurisdiction review | Match the workflow to local law, signer intent, and retention rules |
Leading Platforms and Provider Comparison
Digital signature verification does not end with the viewer. The platform that created the signature determines how much identity evidence, audit history, document routing, and retention support the organization can produce later. No competitor pages are linked in this section; buyers should review current vendor materials through their own procurement process when validating plan-specific claims.
DocuSign for global enterprise signing programs
DocuSign is often evaluated by large organizations that already have legal, procurement, and IT administration resources. It can fit broad enterprise signing programs, but buyers should check plan-level limits, identity verification options, API needs, support model, regional access expectations, and how audit evidence is exported for cross-border records.
Adobe Acrobat Sign for PDF-led signing teams
Adobe Acrobat Sign is commonly considered by teams whose document work already centers on PDFs and Acrobat-style review. It can be convenient for PDF-heavy teams, but buyers still need to confirm signer identity controls, certificate-backed signing levels, regional rollout fit, and whether the audit trail is strong enough for legal or compliance review.
Dropbox Sign for lightweight SMB approval flows
Dropbox Sign is usually a better fit for simpler send-and-sign workflows, small teams, and lower-risk approvals. It may be less suitable when the organization needs deeper certificate validation, advanced identity evidence, APAC legal review, or complex record retention.
Where Nota Sign Fits for APAC-ready verification workflows
Nota Sign is a stronger fit when the workflow needs signer identity evidence, certificate-backed signing, tamper-evident audit trails, signed-record retention, and APAC cross-border readiness. Teams can review the Nota Sign electronic signature workflow and the Nota Sign Trust Center when evaluating whether manual verification is enough or a standardized signing workflow is needed.
The right platform depends on what the organization must prove later. For digital signature verification, the important comparison points are not just price or brand familiarity. They are identity evidence, certificate depth, audit trail quality, regional fit, and whether the signed record can be preserved and retrieved.
| Criteria | DocuSign | Adobe Acrobat Sign | Dropbox Sign | Nota Sign |
|---|---|---|---|---|
| Best for | Large global programs with established admin and procurement resources | PDF-led teams already centered on Acrobat-style document handling | SMB teams with simpler approval flows | APAC-ready and cross-border agreement workflows |
| Setup effort | Medium to high when identity, API, templates, and governance are involved | Medium when PDF workflows, integrations, and admin policies must align | Low for simple send-and-sign workflows | Medium, because document risk, signer regions, identity, and evidence setup should be mapped first |
| Pricing / cost risk | Review seat, envelope, API, identity, support, and contract assumptions privately before rollout | Review plan scope, add-ons, identity controls, and PDF ecosystem dependency | Lower entry cost, but advanced evidence or governance needs may outgrow the tool | Evaluate by signing volume, signer identity needs, APAC support, retention, and onboarding requirements |
| Process / workflow limits | Can be strong for enterprise teams, but configuration and governance may be heavier | Stronger where PDF handling is central; less ideal if the team needs broader regional signing design | Good for lightweight approvals; weaker for complex routing and evidence review | Supports templates, routing, audit records, API-ready workflows, and signer evidence for regional rollouts |
| Identity verification | Plan and region dependent; buyers should verify available ID options | Plan and region dependent; check certificate and identity controls for the target market | Usually lighter identity evidence for routine workflows | Supports stronger signer identity and certificate-backed evidence for higher-risk workflows |
| Audit trail | Platform audit records are available, but review export detail and retention needs | Audit records depend on workflow setup and plan scope | Basic activity history may be enough for low-risk use | Full document history with signer actions, timestamps, authentication events, and exportable evidence |
| Compliance fit | Suitable when enterprise teams configure the right controls for each region | Useful for PDF-heavy compliance processes when controls match the jurisdiction | Better for low-risk documents with limited compliance pressure | Better suited to teams that need SES, AES, QES-level workflow choices and regional compliance review |
| Support / onboarding | Often admin-led and procurement-led | Often IT/document-workflow led | Mostly self-service | Evaluation support for teams mapping documents, signer regions, risk levels, and rollout constraints |
| When to choose it | You already have enterprise resources to manage configuration and cost governance | Your signing program is deeply tied to PDF tooling | The document has low legal or operational risk | You need repeatable signing evidence across APAC and global workflows |
For most teams, the decision is not "viewer or platform." It is whether the business needs a defensible signing process. A viewer can inspect a signature. A workflow platform helps generate the evidence in the first place.
APAC Legal Checks and Platform Workflow Limits
A technically valid digital signature can still be risky if the signing workflow does not fit the jurisdiction, document type, or evidence requirement.
Hong Kong is a good example. The Digital Policy Office explains that the Electronic Transactions Ordinance gives electronic records and electronic signatures legal recognition, while government-entity transactions may require a digital signature supported by a recognized digital certificate. That distinction matters when businesses move from ordinary commercial agreements to higher-assurance or government-facing workflows.
For EU-facing agreements, the European Commission's Digital Signature Service is a useful official reference because it focuses on electronic signature creation and validation in line with eIDAS and related standards.
For APAC cross-border contracts, teams should confirm:
- Which law governs the agreement and which document types are excluded or restricted.
- Whether electronic signatures, digital signatures, or recognized digital certificates are required.
- Whether signer identity verification is strong enough for the transaction risk.
- Whether signed records, audit trails, and certificates of completion are retained in a usable format.
- Whether counterparties in Hong Kong, Singapore, mainland China, or other APAC markets can open, sign, verify, and preserve the agreement without regional access problems.
Legal enforceability depends on more than cryptography. It also depends on intent, consent, attribution, record integrity, retention, and the rules of the market where the document may be challenged.
When manual verification is not enough. Manual verification works for occasional document review. It becomes fragile when teams process many contracts, operate across regions, or need consistent evidence for future disputes.
Move to a standardized signing workflow when:
- Several teams send agreements and need consistent templates.
- Signers are in multiple regions or jurisdictions.
- The document requires stronger signer identity evidence.
- Legal or compliance teams need exportable audit records.
- Signed documents must be retained and retrieved later.
- API or CRM integration is needed to reduce manual handling.
Nota Sign helps teams move from one-off validation into a controlled agreement workflow. Its signing process supports certificate-backed digital signatures, signer identity evidence, audit trails, role-based document routing, and retained signed records, so teams can verify the evidence later instead of reconstructing it after a problem appears.
Final Recommendation
Digital signature verification should not stop at a "valid" status. The real goal is to decide whether your team can trust the file, explain why it can be trusted, and produce the evidence later when legal, compliance, finance, HR, or a counterparty asks for it.
Start with the technical layer: certificate, integrity, revocation status, timestamp, and validation result. Then review the business evidence: signer identity, signing intent, workflow history, audit trail, and document retention. A routine PDF may only need manual review. APAC cross-border contracts, regulated approvals, and high-value agreements are better handled through a platform workflow that completes signing and preserves evidence from the beginning.
If your team needs a more reliable way to sign, verify, and retain evidence, bring your actual workflow to a Nota Sign review: signing volume, signer regions, identity verification requirements, audit needs, templates, integrations, and retention rules all shape the right setup. Talk to Nota Sign Sales to map the signing workflow before you standardize it.